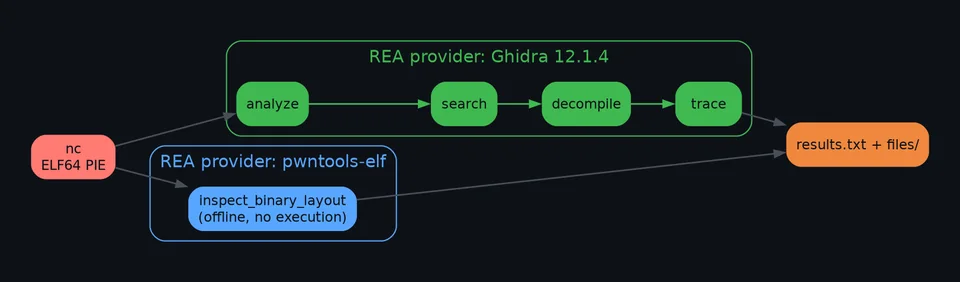
An author-published static investigation of a Linux netcat binary, with REA evidence files, Ghidra findings and cross-checks against standard binary tools.
Analysis only
Sources & limits +
Author documents REA use
The repository names REA 6.2.0 and Ghidra 12.1.4 and links its raw analysis artifacts. Its reported findings are static, not a runtime test.
Know before you try: The target is already open source. This is a research write-up, not a new netcat implementation or proof that a binary is safe.
The upstream toolkit connecting coding agents to binary, application and runtime investigations through MCP and a command-line interface.
Actively developed toolkit
Sources & limits +
Upstream REA project
The upstream README documents rea-agents setup, supported targets, analysis providers and evidence-carrying workflows. This is the original project, not an unofficial mirror.
Know before you try: Provider and platform requirements vary. Local analysis does not mean the coding agent's model provider receives no data. Check current upstream requirements.
Google Analytics loads only if you allow it. It uses cookies to measure page visits, without sending search terms. Declining does not affect the directory. Privacy details